Tag: victims

  • Criminals target previous scam victims

    Criminals target previous scam victims | Australian Broker News

    News

    Criminals target previous scam victims

    New scams promise monetary restoration – for a charge
    Criminals target previous scam victims

    The National Anti-Scam Centre warns Australians who’ve misplaced cash to scammers to beware of recent scams promising monetary restoration for an upfront charge.

    Reports involving restoration scams have surged, with Scamwatch receiving 158 reviews totaling over $2.9 million in losses between December 2023 and May.

    Despite a 129% improve in reviews, monetary losses decreased by 29% from $4.1m.

    Targeting the weak

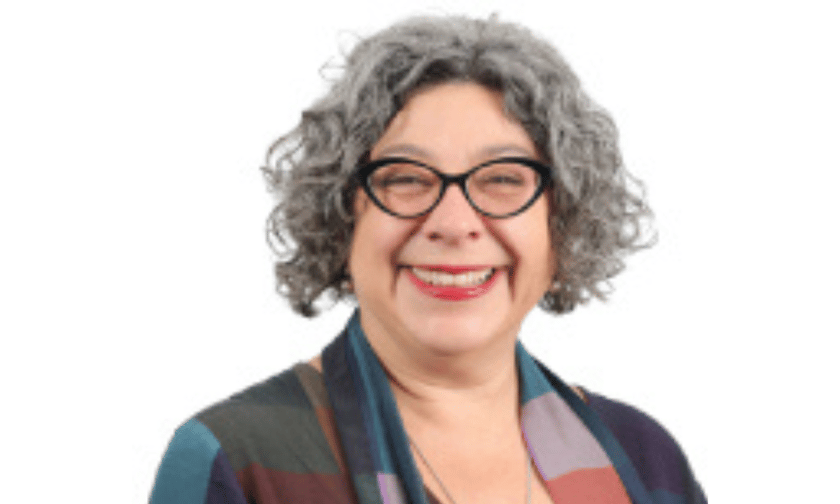
    “Money restoration scams are damaging and merciless. Criminals prey on individuals who have already been victims of a scam who hope to get their a reimbursement,” ACCC deputy chair Catriona Lowe (pictured above) mentioned.

    Australians aged 65 and older reported the very best losses. Scammers usually pose as trusted entities, together with authorities businesses, attorneys, and even charities, to use victims additional.

    Rising scam risk

    Scammers use varied strategies to contact victims, together with e mail, telephone calls, and social media. They promise to get well losses for an upfront charge or a share of the recovered funds, usually requesting private info or distant entry to gadgets.

    “We are very involved about revictimisation, which might compound each the monetary and emotional hurt brought on by scams,” Lowe mentioned.

    Proactive measures

    In response, the National Anti-Scam Centre has taken down two web sites concerned in restoration scams.

    Victims are suggested to not have interaction with anybody promising to get well stolen cash and to report scams to the police and their monetary establishments.

    “Scams are crimes, and the criminals who prey on determined folks attempting to get well within the aftermath are reprehensible,” Lowe mentioned.

    How restoration scam works


    Contact: Scammers pose as trusted entities and phone victims by way of varied channels.
    Promise: They supply to get well losses for an upfront charge or a share of the recovered quantity.
    Information: Scammers ask for private info or distant entry to gadgets.
    Deception: They present faux suggestions or opinions to look official.

    Protect your self

    To keep away from falling sufferer to those scams, observe these steps:


    Stop: If contacted with a proposal to get well cash for a charge, it’s a scam.
    Check: Verify the id of the contact by utilizing independently sourced contact info.
    Protect: Do not give out private or monetary info or permit distant entry to your gadgets.
    Report: Report scams to the police and your monetary establishment.

    Background and recommendation

    The National Anti-Scam Centre notes that solely legislation enforcement can seize and get well belongings.

    The centre cautions towards partaking with companies providing restoration providers, as these usually include excessive prices and unlikely outcomes.

    “Anyone will be scammed, and that’s one of many causes drawing consideration to Scamwatch’s recommendation and sources is so essential,” Lowe mentioned.

    Get the most popular and freshest mortgage information delivered proper into your inbox. Subscribe now to our FREE each day e-newsletter.

    Related Stories

    Keep up with the most recent information and occasions

    Join our mailing checklist, it’s free!
  • Snowflake facts breach victims possible impacted mortgage creditors

    The guidelines of victims of a cybersecurity incident tied to extensively used cloud storage firm Snowflake may embody property finance mortgage firms, specialists say.

    The cloud information platform and Google-owned cybersecurity agency Mandiant stated they’ve notified 165 unnamed, most definitely uncovered firms. The Montana-based Snowflake was not hacked, however cybercriminals made use of stolen {qualifications} to infiltrate information belonging to companies, which allegedly entails Ticketmaster.

    The unidentified danger actors are additionally auctioning off on cybercriminal neighborhood boards purchaser information from LendingTree subsidiary QuoteWizard, a useful resource instructed Coverage Journal. LendingTree didn’t reply to a request for comment Wednesday. 

    No dwelling finance mortgage enterprises have publicly disclosed an impression from the Snowflake incident. Mortgage mortgage technological innovation leaders even so is not going to really feel the enterprise is totally immune. 

    “Just the straightforward indisputable fact that the system is so substantial and so expansive, I might uncover it fairly troublesome to contemplate that you can find not at minimal 1 lender that takes benefit of it,” talked about Matt Lehnen, chief technological know-how officer at Deephaven Home mortgage.

    Jason Bressler, predominant know-how officer at United Wholesale Home finance mortgage, really useful a number of mortgage mortgage organizations use Snowflake.

    “It has the chance and the likelihood to change into the premier cybersecurity breach in firm The us document,” he reported.

    Each CTOs defined their firms is not going to use Snowflake. Home mortgage corporations at the moment are reeling from a spate of cybersecurity incidents within the earlier 12 months which have affected tens of tens of millions of customers and cost tons of of hundreds of {dollars} to deal with.

    Mandiant in its extended see with Snowflake attributed the authorized conduct to a “monetarily motivated risk actor” making an attempt to extort victims in exercise beginning in April. Hackers reportedly obtained credentials by the use of malware from contractors which customers made use of to information with their use of Snowflake.

    Impacted accounts didn’t have multi-issue authentication enabled, and a few compromised accounts had the exact same login because of the reality their theft as significantly once more as 2020, the report stated. 

    Snowflake has not disclosed the extent of the data theft. A advisor for the company Wednesday responded to an inventory of questions with a web site hyperlink to Snowflake’s updates on its investigation.

    The hackers, acknowledged within the Mandiant report as “UNC5537” are functioning beneath aliases on social media system Telegram and different cybercrime message boards. The criminals are dependent within the United States, and on the very least one collaborator depends in Turkey, Mandiant acknowledged with reasonable self worth. They are allegedly storing stolen information on intercontinental digital private servers and file internet hosting service Mega.

    Michael Nouguier, predominant particulars safety officer and director of cybersecurity skilled companies at Richey Might, defined Snowflake as a facts administration chief unsuccessful to current administration in imposing stronger cybersecurity controls.

    “The precept of choose-out safety isn’t changing into leveraged proper right here,” he claimed. 

    Nouguier in contrast decide-out security to decide-in stability, precisely the place finish customers are accountable on their very own for enacting actions this kind of as MFA. He pointed to GitHub, the popular developer system, as an illustration of a excellent area platform which executed MFA specs.

    Snowflake in its updates defined it’s now creating a method to demand buyers to make use of MFA or community insurance coverage insurance policies, one more cybersecurity measure. 

    Jim Routh, predominant depend on officer at applied sciences agency Saviynt, additionally predicted the Snowflake incident will have an effect on a number of organizations. He claimed firms, specifically cloud pc software program suppliers, have elected to stick with particular person ID and password credentials somewhat than progressive authentication alternate options due to a “confined market drive” to go off them. 

    “Passwords have served the market correctly for above sixty a number of years, however they weren’t created to be used all through tons of of digital property that a number of digital prospects and workforce will want,” he talked about in an email correspondence. “The advantages embody consumers and consumers that resolve on the identical password for a number of digital belongings increasing the affect when {qualifications} have been compromised.”